Build Docker image
Buddy lets developers build Docker images with code from a Git repository and the selected Dockerfile. Setting up a Docker-focused pipeline is as easy as setting up any other type of delivery in the service.
Configuration
- First, you need to specify which repository should the image be based on. Buddy has native integrations with GitHub, Bitbucket and GitLab, but you can hook up any other repository as well:
Image loading...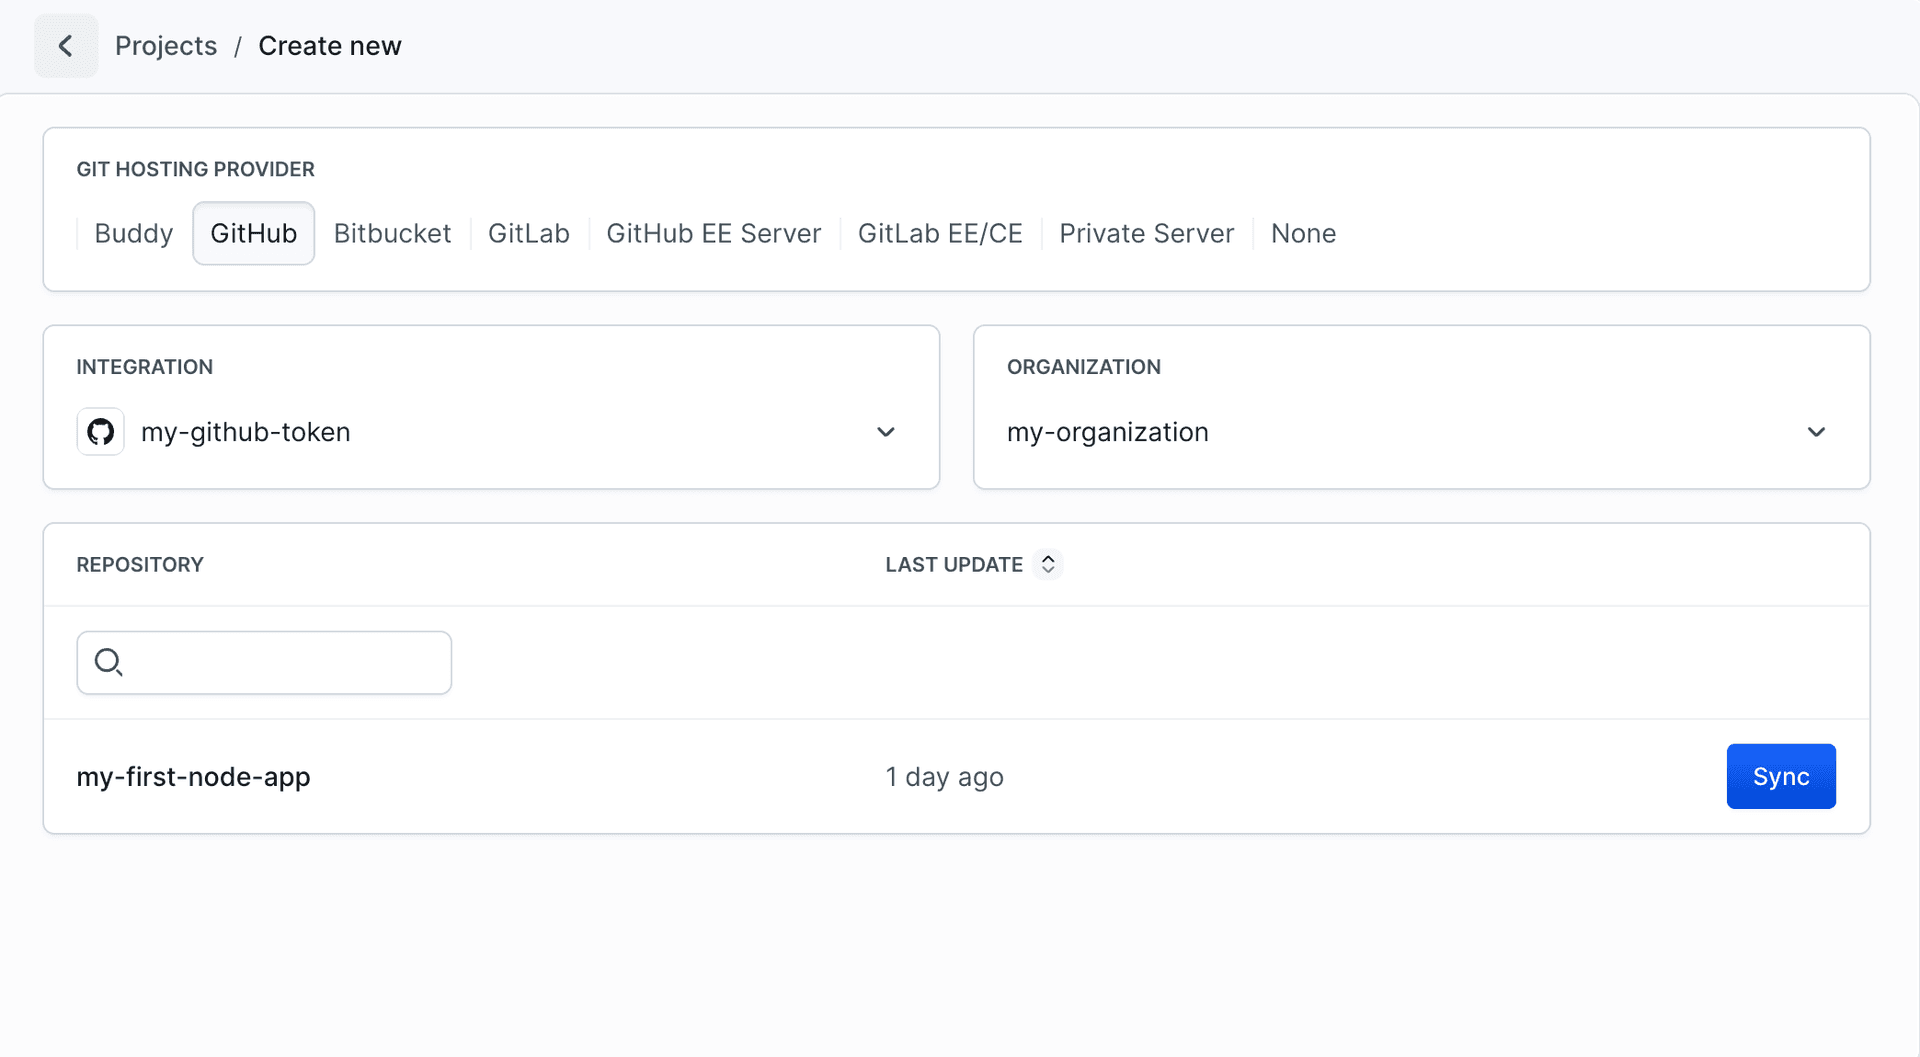
- With the repository successfully synchronized, you can add the pipeline:
Image loading...
After creating the pipeline, you can configure when it should run by setting up triggers in the workflow. You can trigger pipelines on Git push events, webhooks, scheduled intervals, or manually. Learn how to configure pipeline triggers.
Image loading...
- With the pipeline prepared, we can add the Build Image from the Docker section of the action roster:
Image loading...
- In the action configuration, you can specify:
- Pull required images or push image after built: Enable private registry authentication
- Build Dockerfile: Path to your Dockerfile (default:
Dockerfile) - Context: Directory containing the build context (default:
/) - Build arguments: Add build-time arguments using the + button
- Secrets: Add secrets for the build process using the + button
- Options: Configure additional build options (e.g., "Always attempt to pull a newer version of the image")
- Push image to registry: Enable automatic push after building
Image loading...
Building private images
If the image is private (e.g. FROM: my-registry.com/buddy/my-image:latest) and requires logging into a registry, you can configure the integration in the Build tab in the action.
Buddy natively integrates with Docker Hub, Amazon ECR, Google GCR, GitHub Container Registry, Google Artifact Registry, DigitalOcean Container Registry, and other registries. You can also use any other private registry:
Image loading...
Building Multi-Arch Docker images
The Multi-Arch Build Image action allows you to set the target architecture for which the Docker image is built:
- linux/amd64
- linux/arm64
- linux/arm/v7
- linux/arm/v6
To choose the platform, add the action to the pipeline and select the desired architectures in the Platform section:
Image loading...
Docker image Continuous Delivery
With Buddy, you can automate basically any type of DevOps process. For example, you can create a pipeline that will perform the following tasks on every push to the selected branch – just by adding new actions to the already existing ones:
- Run unit tests
- Check the Dockerfile for issues
- Build a Docker image
- Run the image and test it for errors
- Push the image to the selected registry
- Send a notification to a Slack channel
Here's how these tasks look like transferred into pipeline actions:
Image loading...
Build arguments
By default, Buddy doesn't pass the environment variables to the build. If you want to pass them, you have to define build args and provide the environment variable that you want to pass as a value.
Apart from this, you can define your own build arguments in the action:
Image loading...
docker history, and Docker reports them with the SecretsUsedInArgOrEnv warning. Use build secrets instead.
Target build stage
If your Dockerfile contains multiple build stages, you can specify which stage should be built using the --target option. This will skip all commands after the target stage. You can configure this in the Options section:
Image loading...
Provenance
In the Build Docker image action, you can enable the creation of provenance attestations. These attestations encompass essential data, such as build timestamps, build parameters and environment configurations, version control metadata, and source code details. To utilize the feature, add the option in the Options section and select the desired mode from the dropdown:
Image loading...
Build secrets
Build secrets pass an npm token, a .npmrc file, or other credentials to RUN instructions without storing them in the image. Unlike build arguments, they do not appear in image layers or in docker history.
Click the + button in the Secrets section to choose from two methods:
- Add secret with variable as source: Use an environment variable as the source for your secret. In Value, enter the variable name without
$, for exampleNPM_TOKEN. Use only letters, digits,_,-, and., or the action will not save. - Add secret with file as source: Use a file from the filesystem as the source for your secret. In Value, enter the path to the file.
Each secret has a Secret ID, for example npm_token. You reference it in the Dockerfile.
Image loading...
To use a secret, mount it in a RUN instruction of your Dockerfile. The id must match the Secret ID set in the action. The secret is available as a file in /run/secrets/<id> only while that instruction runs, so it does not end up in the image layers. The action builds with BuildKit (docker buildx build), so you do not need to set DOCKER_BUILDKIT=1:
RUN \
NPM_TOKEN=$(cat /run/secrets/npm_token) npm ci
To mount a file secret, such as .npmrc, at the path the tool expects, add target:
RUN npm ci
To expose the secret as an environment variable instead, add env, for example --mount=type=secret,id=npm_token,env=NPM_TOKEN. This option requires Dockerfile syntax 1.10 or later, so start the Dockerfile with # syntax=docker/dockerfile:1.
In YAML, secrets are defined in the secrets list of the action:
secrets:
- id: npm_token
  type: ENV
  value: NPM_TOKEN
See Build secrets in the Docker documentation for more options.
Cache
All Docker layers are automatically cached during the build process. This caching mechanism ensures that future builds only create layers that have been modified since the last build, which drastically reduces the build time.
You can configure additional cache-related settings by adding options in the Options section:
- Always attempt to pull a newer version of the image: This option ensures that Buddy always tries to pull the latest version of base images before building
- Prune dangling images: While it is possible to prune dangling images, we do not recommend doing so as it may slow down subsequent builds
Image loading...
📚 Learn more about Build Docker image action features, integrations and alternatives.
YAML and API
- YAML configuration - Build Docker image configuration via YAML
- REST API - adding the action via API
Last modified on Nov 17, 2026